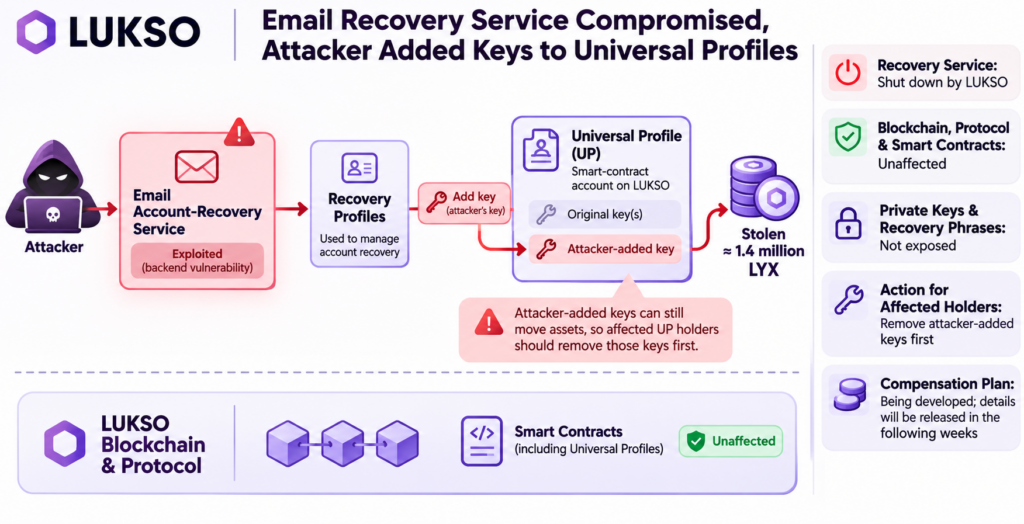
For affected Universal Profile holders, the immediate task was to remove attacker-added keys: LUKSO warned that those keys could still move assets left in the accounts. Universal Profiles are smart-contract accounts on LUKSO.
As reported on November 19, 2026, PANews, citing The Defiant, said LUKSO had disclosed an attack during the night of November 17–18. According to LUKSO, an attacker exploited a backend vulnerability in its email account-recovery service and took control of recovery profiles. The attacker then used those profiles to add their own keys to about 300 Universal Profiles and steal approximately 1.4 million LYX.
LUKSO said it had shut down the recovery service. It also said the blockchain, protocol and smart contracts were unaffected, and that private keys and recovery phrases had not been exposed. The reported point of failure was the recovery service that could add account keys, not the underlying contracts. LUKSO said it was developing a compensation plan and would release details in the following weeks.