Operators of LNbits servers were urged to update to version 1.7.0 and check whether their credentials had been exposed. As reported on November 11, 2026, the Bitcoin Lightning wallet platform said attacks on LNbits installations had resulted in stolen funds.
LNbits released the critical update on November 10. It said the vulnerability affects all earlier versions and puts funds at risk. The release also strengthens authentication, extension management and payment handling, but LNbits warned that updating alone will not secure credentials already compromised.
The project first told operators on November 8 to disable its Paywall extension while it investigated a potential vulnerability. Just over an hour later, it urged them to shut down their LNbits servers, citing a wave of attacks, and took its own hosted installations offline.
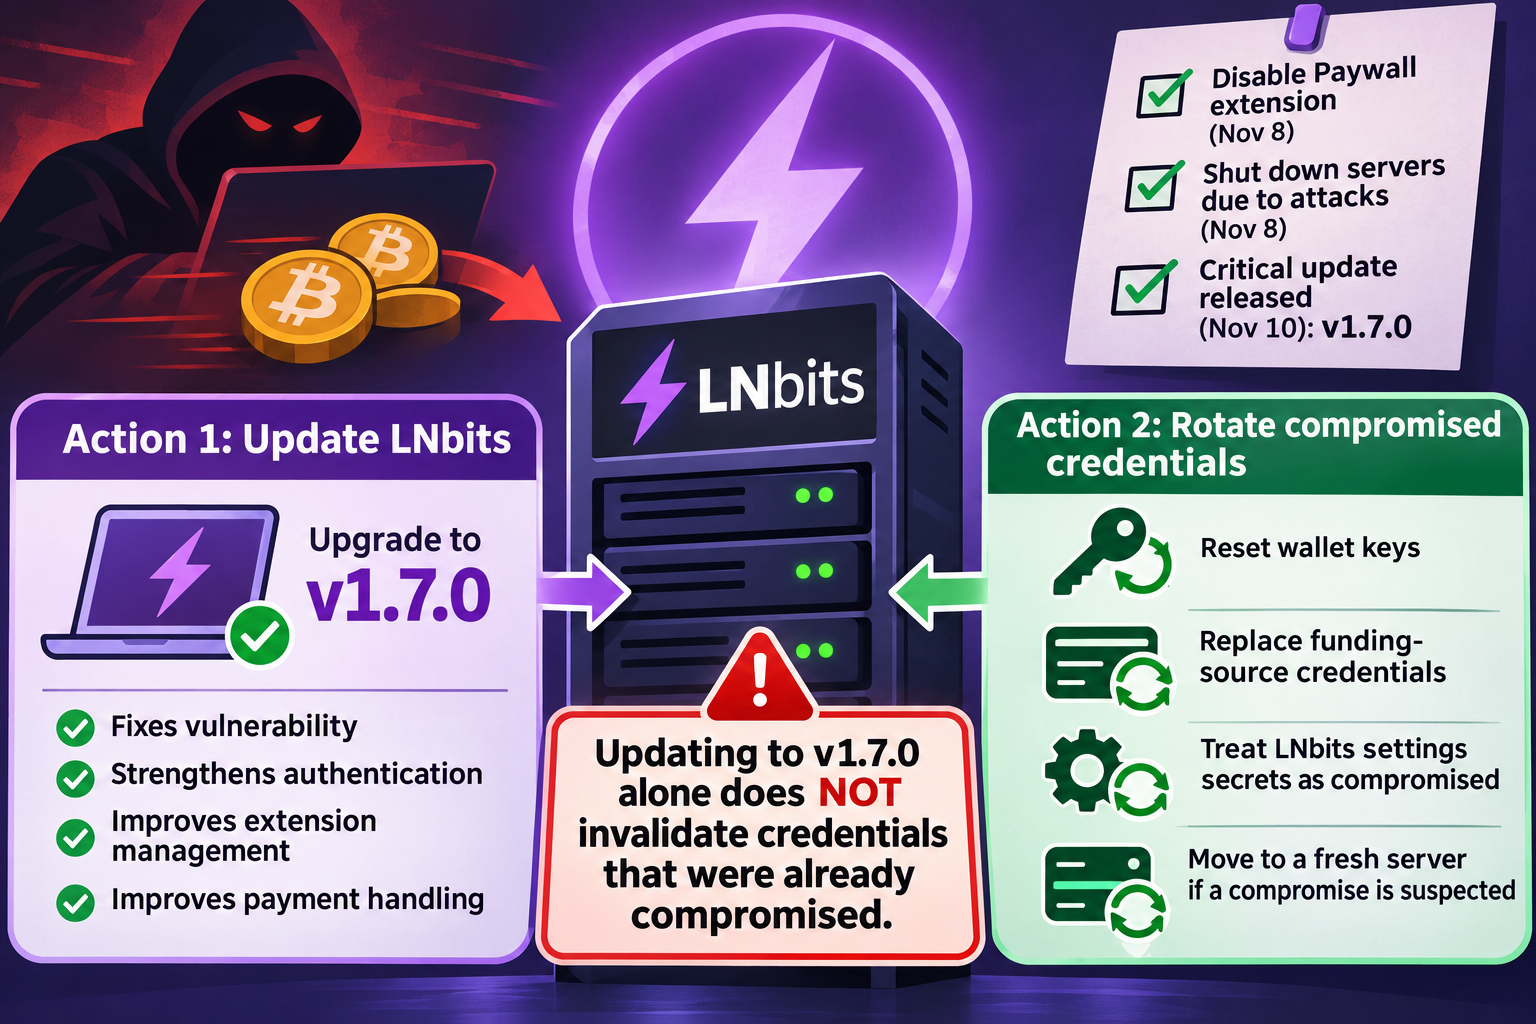
For operators, LNbits recommended resetting wallet keys, replacing funding-source credentials and treating secrets stored in LNbits settings as compromised. It also recommended moving to a fresh server if a compromise is suspected. The project had not yet explained how the exploit worked or how many installations were affected; it said a separate report would follow.
One user, Kevin Ravensberg, said attackers created accounts on his LNbits instance and withdrew about 2.3 million satoshis (0.023 Bitcoin) before he could shut down the server. That is his account of the loss, not a total for the attacks. LNbits creator Ben Arc said the project and its users had suffered losses while the team worked on the release.