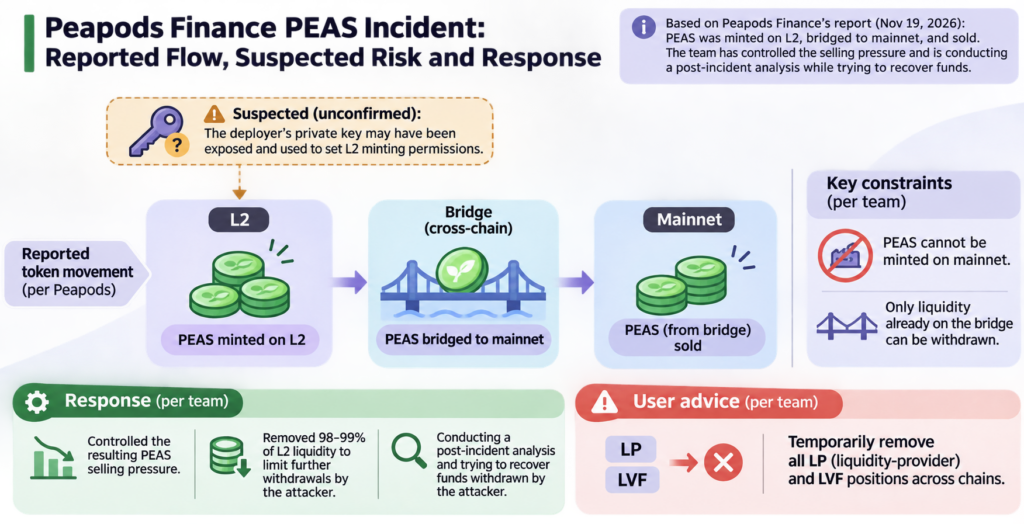
For builders managing token permissions across chains, the key question in the PEAS incident is how minting authority was set on L2. In a report published on November 19, 2026, Peapods Finance said PEAS had been minted on L2, bridged to mainnet and sold. Its preliminary assessment was that the deployer’s private key may have been exposed and used to set L2 minting permissions. The suspected key exposure has not been confirmed.
Peapods said it had brought the resulting PEAS selling pressure under control and removed 98–99% of L2 liquidity to limit further withdrawals by the attacker. According to the team, PEAS cannot be minted on mainnet; only liquidity already on the bridge can be withdrawn. It was conducting a post-incident analysis and trying to recover funds withdrawn by the attacker.
The team advised users to temporarily remove all LP (liquidity-provider) and LVF positions across chains.